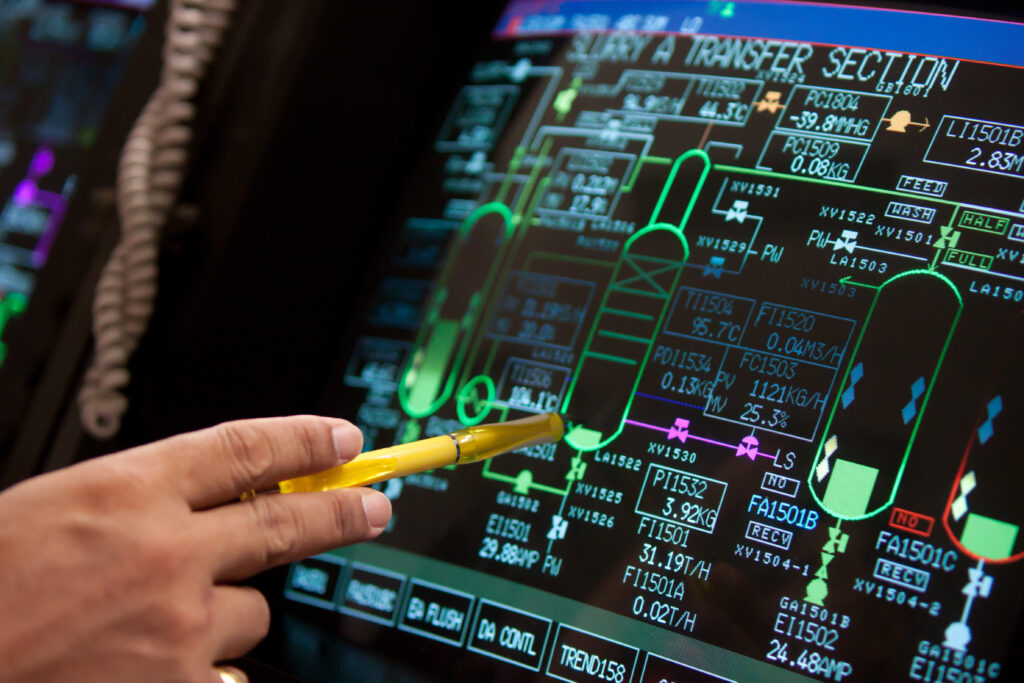
Test OT cyber defences with a methodology designed to protect safety, reliability and live operations.
Many organisations need assurance that OT systems, network boundaries and remote access pathways can resist cyber attack. But conventional penetration-testing approaches can create unacceptable risk in operational environments, where aggressive scanning, uncontrolled exploitation or poorly timed testing may affect safety systems, communications, control processes or service continuity.
OT testing needs to account for the environment before technical activity begins. Long-life assets, legacy protocols, vendor-supported systems, restricted maintenance windows and dependencies between operational services all shape what can be tested, when it can be tested and how findings should be validated.
Without an OT-specific approach, testing may either introduce unnecessary operational risk or remain too limited to provide meaningful assurance. Teams can receive generic technical findings without a clear view of exploitability, operational consequence or the practical actions required to reduce exposure.
Implicit OT delivers penetration testing through a controlled, risk-informed approach designed for operational technology environments. We work with asset owners, engineering, operations, cyber and relevant vendors to define the scope, objectives, rules of engagement, safety constraints and escalation pathways before testing begins.
We assess the pathways an attacker could use to gain access, move through the environment or affect critical systems. Testing may include external exposure, remote access, IT/OT boundaries, network segmentation, identity controls, configuration weaknesses and selected OT systems, only where activity is authorised and safe.
Our engineering-led approach provides meaningful assurance without treating live operations as a test environment. We validate findings carefully, explain their operational significance and provide practical remediation priorities that can be delivered through planned changes, projects and maintenance activity.
Controlled testing of OT environments to identify exploitable weaknesses while respecting approved scope, safety requirements and operational constraints.
Assessment of internet-facing systems, remote-access services and exposed pathways that could provide an attacker with an entry point to OT-connected environments.
Testing of security controls and pathways between enterprise IT, OT networks, DMZ services and supporting infrastructure.
Assessment of employee, contractor and vendor access pathways, including authentication, authorisation, segmentation, session controls and monitoring.
Validation of whether OT network boundaries, firewall rules and controlled conduits limit unnecessary access and lateral movement as intended.
Clear findings, practical remediation advice and targeted retesting to confirm priority weaknesses have been addressed.
Share your environment details. We’ll come on‑site to design a security program that fits your operations, not fights them.