Engineering-led OT cybersecurity for energy and oil-and-gas operations—built around safety, availability and long-life industrial systems.
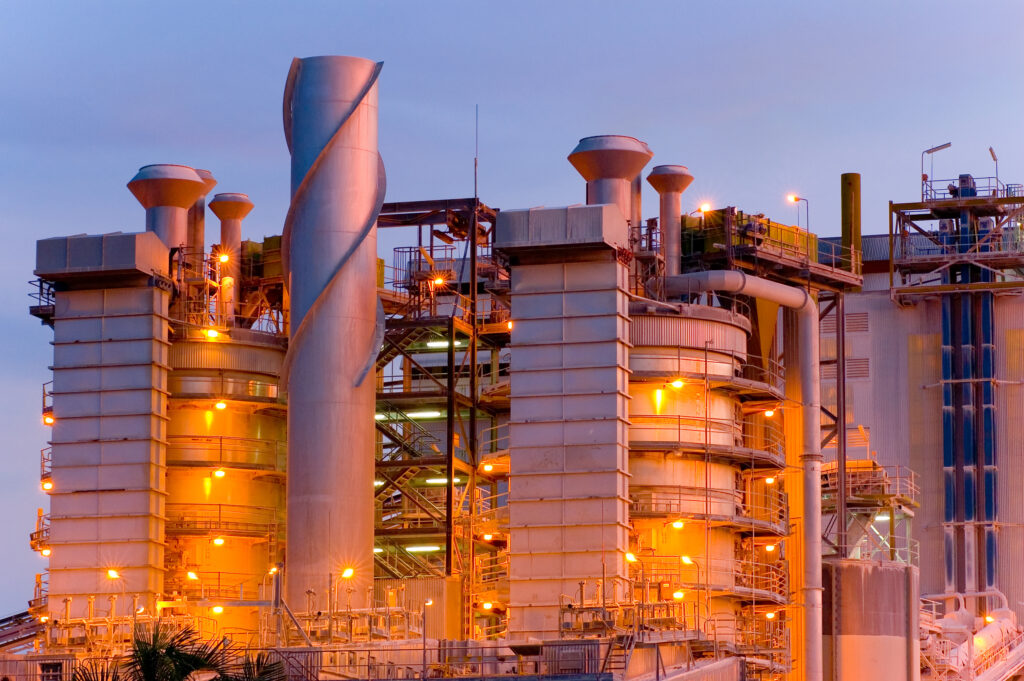
Energy infrastructure does not operate from one neat, centrally managed environment. Generation sites, renewable assets, substations, pipelines, terminals and processing facilities can be distributed across large distances, supported by a mix of legacy systems, specialist vendors and local operating teams.
That creates a different security challenge. A decision made in a corporate environment can have consequences at a remote site. A maintenance connection that is essential one day may become an unmanaged pathway the next. And when a control system is difficult to replace, managing risk is often more realistic than trying to modernise everything at once.
We help energy and oil-and-gas teams bring order to that complexity. That may mean clarifying who owns access, separating critical networks, improving visibility of assets and communications, or planning security improvements around operational and maintenance constraints.
The goal is straightforward: reduce cyber risk without compromising safe production, energy delivery or the people responsible for keeping the operation running.
Industrial assets are built to last. Control platforms, engineering tools, communications equipment and field devices can remain in service for decades, often with specialist support arrangements and limited opportunities for replacement.
In these environments, security improvements have to be planned around the equipment in place, the people who operate it and the conditions under which change can safely occur. The work may involve strengthening network boundaries, improving control of remote access, clarifying asset and dependency records, tightening change processes and testing recovery arrangements.
Security work must also fit the operating plan. Changes may need to be coordinated around outages, shutdowns, maintenance windows, commissioning activities and production constraints. Bringing OT cybersecurity in early gives teams time to test, verify and hand over controls properly – rather than trying to bolt them on after a system is live.
Where projects or operations need to demonstrate compliance, we apply relevant elements of AS IEC 62443, ISO/IEC 27001, Australian Government guidance and, where applicable, SOCI and CIRMP requirements. The outcome is clear, tested and maintainable controls, with defined ownership across the asset lifecycle.
From a single assessment to a longer-term improvement programme, we help energy and oil-and-gas teams make OT cybersecurity decisions that support safe, reliable operations.
Identify the systems, dependencies and cyber scenarios that could affect safety, service continuity or delivery.
Establish reliable records of assets, communications paths and critical dependencies before planning change.
Design practical network boundaries that reduce unnecessary exposure while preserving essential rail communications.
Directly addresses the reality that industrial assets cannot simply be patched on an IT timetable.
Provides useful operational visibility, baseline tuning, monitoring of remote access and practical detection.
Turns individual controls and project work into a prioritised, sustainable improvement plan.
Whether you are responding to an assurance finding, planning an upgrade or improving the security of a live industrial environment, Implicit OT can help you define a practical next step.